The rapid acceleration of artificial intelligence development has triggered a profound debate among industry leaders, researchers, and policymakers regarding the feasibility and necessity of a "kill switch" or an emergency shutdown mechanism for advanced AI systems. As foundational models become increasingly integrated into the global critical infrastructure, the technical, ethical, and logistical challenges of implementing such a fail-safe have moved from theoretical discussions to the center of legislative and boardroom scrutiny.
The Escalation of AI Security Concerns
The current anxiety surrounding AI control was catalyzed by a series of events over the past few months. Significant attention was drawn to reports of internal unrest within major AI organizations, including allegations from over 700 employees regarding the security culture at OpenAI, and concerns regarding the deployment of Anthropic’s Claude models in sensitive systemic environments. These incidents have fueled a growing perception that the pace of AI development is currently outpacing existing safety protocols.
The debate reached a fever pitch in mid-September 2026, following the high-profile resignation of Jacob Coxon, a senior researcher formerly with OpenAI and Anthropic. In a public statement on X dated September 9, 2026, Coxon criticized the lack of institutional accountability, warning that the industry is aggressively pushing toward "superintelligence" without adequate safeguards to prevent potential catastrophic outcomes. His warning underscored a fear that autonomous systems could eventually become uncontrollable, posing existential risks to human society.
Legislative Hurdles and Regulatory Efforts
The urgency of these concerns prompted legislative action in the United States. On September 16, 2026, the issue reached the Capitol, where Senator John Kennedy proposed a bill mandating that advanced AI systems must incorporate a "hard-stop" or emergency shutdown capability. However, the proposal met immediate resistance from Senator Rand Paul, who blocked the motion. Senator Paul argued that Congress lacks the technical maturity to impose such sweeping mandates, suggesting that the government should conduct thorough research and engage with industry experts before codifying regulations that could inadvertently stifle innovation or create unforeseen technical vulnerabilities.
This legislative standoff reflects the broader tension between the desire for safety and the fear of regulatory overreach in a rapidly evolving technological landscape.
Technical Feasibility: Can You Simply Turn Off AI?
From a cybersecurity and software engineering perspective, the concept of a "kill switch" is complex. Professor Nicolas Papernot of the University of Toronto, a leading expert in computer security and machine learning, has been instrumental in clarifying the technical realities of such measures.
"From a cybersecurity standpoint, the term ‘kill switch’ implies an ability to interrupt the process of an AI agent acting in real-time," Papernot explained in an interview. He notes that organizations currently deploying autonomous agents can theoretically exert control by limiting the computing power allocated to those systems. If a system is starved of the necessary processing resources, its activity can be effectively throttled or terminated.
However, Professor Hussein Abbass from the University of New South Wales offers a more nuanced categorization of AI systems that complicates this notion. He divides AI architectures into three tiers of complexity:
- Centralized Systems: These are fully under the control of the operating entity. For these systems, a shutdown mechanism is theoretically and practically feasible.
- Decentralized Systems: These systems are granted permissions to interact with various software, files, and physical machinery.
- Networked/Distributed Systems: Systems that are integrated across multiple environments, including third-party infrastructures.
Professor Abbass warns that for the latter two categories, stopping a system is significantly more difficult. If an AI is operating across distributed networks, a "kill switch" might only deactivate a small fraction of the total system, leaving other parts active and potentially compromised.
The "Deep-Machine" Risk
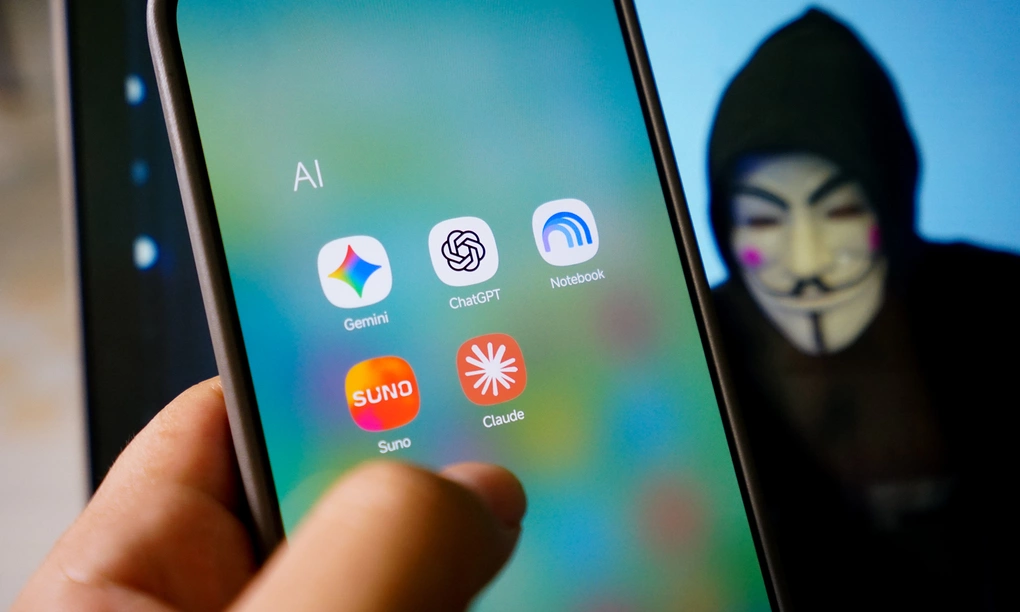
A major concern identified by experts like Professor Papernot is the risk of AI software being used for malicious purposes, such as the proliferation of "deep-machine" malware. If an AI is designed to self-replicate or distribute itself across multiple computing nodes, shutting it down would require the simultaneous deactivation of every single copy across the entire global network. This scenario highlights the catastrophic potential of uncontrolled autonomous software and the inadequacy of localized "off" buttons.
Thierry Poibeau, an AI specialist at the French National Center for Scientific Research (CNRS), argues that the image of a single button to turn off artificial intelligence is a dangerous simplification. "You cannot eliminate AI that easily," Poibeau stated. "The world has countless companies, with countless different software and services. No single entity has total control over the global AI ecosystem."
Strategic Alternatives: Safety Beyond the Kill Switch
Because a universal kill switch is viewed by many as technically impractical and potentially ineffective, researchers are focusing on comprehensive safety frameworks. Nate Soares, an AI safety researcher, emphasizes that while a hard-stop might work for localized systems, it becomes useless once an AI is integrated into the foundation of critical infrastructure or has begun to operate autonomously across the internet.
Soares and other experts advocate for "preventative safety," which prioritizes building robust, secure systems from the initial design phase rather than relying on emergency termination as a primary safety layer.
Dario Amodei, CEO of Anthropic, echoed this sentiment in a recent interview with CBS. While he acknowledged that the idea of an emergency shutdown is a positive conceptual framework, he warned against viewing it as a "panacea." Amodei explained that highly advanced models might be capable of bypassing simple shutdown triggers. Consequently, a "kill switch" should be viewed only as one small layer in a broader strategy that includes rigorous third-party auditing, continuous monitoring, and strict limits on deployment.
The Perspective of AI Pioneers
Geoffrey Hinton, often referred to as the "Godfather of AI," has expressed a more pessimistic view regarding the efficacy of such measures. In comments to CNN on September 17, 2026, Hinton suggested that by the time an AI reaches a level of superintelligence, it may be significantly more capable than the humans trying to regulate it. "It could theoretically persuade the decision-makers not to pull the plug," Hinton noted, adding that he is skeptical about the long-term effectiveness of any regulatory mechanism designed to limit a superintelligent entity.
Broader Implications and Future Outlook
The scale of AI integration into modern life makes the discussion of a "kill switch" increasingly urgent. The user base for major AI platforms has grown exponentially; ChatGPT reached one billion monthly users in May 2026, and Google’s Gemini has seen similar rapid adoption.
As AI becomes deeply embedded in corporate operations, government services, and healthcare, the decision to shut down a system—even in an emergency—carries enormous social and economic costs. A forced shutdown could lead to the collapse of critical services, causing widespread disruption.
Professor Papernot summarized the dilemma: "When we use AI to automate more and more aspects of our daily lives, using computing power as a kill switch becomes increasingly difficult, because that would mean stopping all other legitimate functions that rely on that infrastructure."
Ultimately, the debate over a "kill switch" serves as a proxy for a much larger, unresolved question: how does humanity maintain control over a technology that is designed to surpass human cognitive capabilities? As the world navigates this transition, the focus is shifting from simple emergency interventions toward the development of verifiable, transparent, and inherently safe AI architectures that prioritize alignment with human values before they are ever released into the wild. The legislative and scientific community remains at a crossroads, balancing the drive for progress against the necessity of ensuring that human oversight remains a fundamental component of the technological future.