Wave of Sophisticated Cyberattacks Targets Critical Infrastructure and Financial Institutions Across Europe

The European digital landscape is facing a severe period of volatility as a coordinated wave of sophisticated cyberattacks continues to compromise critical infrastructure, financial institutions, and public service providers. Over the past several weeks, a series of high-profile security breaches has exposed vulnerabilities in systems ranging from banking networks to climate control infrastructures in retail sectors. These incidents have prompted an urgent, unified response from European Union authorities and cybersecurity agencies, who are scrambling to identify the origins of these threats and harden the continent’s digital defenses against an increasingly capable and persistent adversary.
The Breach at Credit Mutuel Arkea
The most recent high-profile target is the French banking institution Credit Mutuel Arkea. On November 4, 2026, the bank publicly acknowledged that it had fallen victim to a targeted cyber intrusion. According to initial findings, unauthorized actors gained access to specific customer accounts, facilitating the illicit transfer of funds to external banking platforms. The stolen capital was subsequently converted into various cryptocurrencies on several trading exchanges, a common tactic used to obscure the trail of illicit financial flows.
Credit Mutuel Arkea has stated that its security protocols managed to intercept a significant portion of the fraudulent transactions, and the bank is currently engaged in efforts to recover the remaining stolen assets. Contrary to circulating rumors that suggested losses reaching $133 million, the bank clarified that the actual impact on its financial stability is minimal. Furthermore, the institution emphasized that its primary financial assets and the broader integrity of customer holdings remain secure.
The bank categorized the incident as a highly sophisticated "external" attack, explicitly refuting allegations that the breach was facilitated by human error or internal negligence. In response to the gravity of the situation, the Paris prosecutor’s office has initiated a formal investigation into the matter, treating the breach as a significant criminal event.
Chronology of Escalating Cyber Aggression
The attack on Credit Mutuel Arkea does not exist in a vacuum; it is the latest in a rapid succession of digital assaults that have crippled systems across Europe throughout late October and early November.
The timeline of these events suggests a pattern of opportunistic and targeted testing of European network resilience:
- Late October 2026: A wave of cyberattacks hit hundreds of retail stores in France, causing significant operational disruptions.
- November 1, 2026 – November 2, 2026: Three major French blood banks reported system disruptions. While the French Ministry of Health confirmed that the integrity of stored blood supplies remained uncompromised, the incident sparked national concern regarding the safety of medical infrastructure.
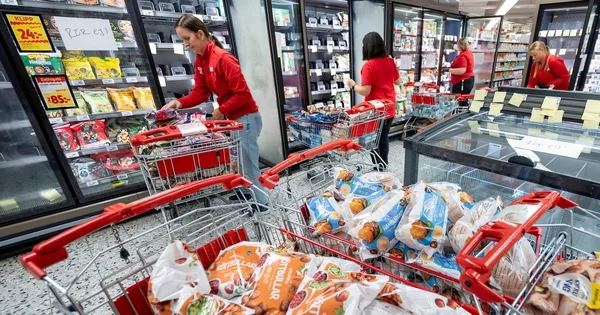
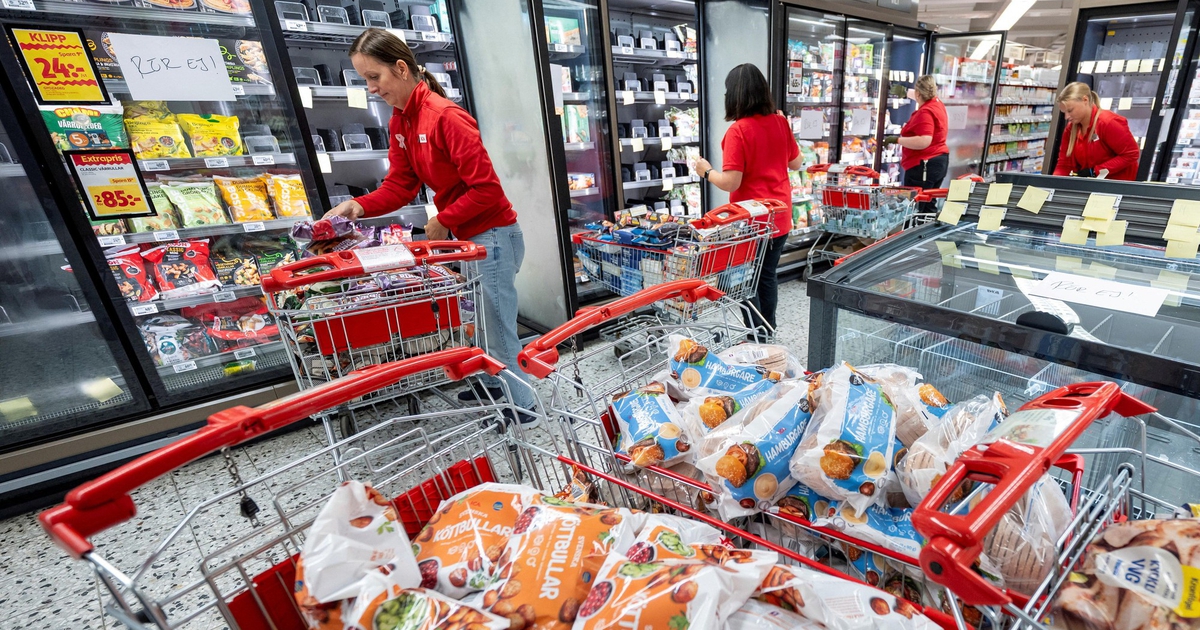
- November 2, 2026: A retail location of the supermarket chain ICA Kvantum in Sjobo, Sweden, suffered a catastrophic systems failure. Hackers gained control of the store’s smart climate control systems, intentionally elevating temperatures to 50 degrees Celsius (122 degrees Fahrenheit). This resulted in the spoilage of perishable goods valued at millions of euros.
- Early November 2026: A massive, unrelated theft of $6.3 billion in digital assets from the Binance exchange earlier in the month created a backdrop of heightened alert across the global financial sector, drawing focus to the massive vulnerabilities inherent in decentralized finance and large-scale digital banking infrastructure.
The Vulnerability of Internet-Connected Infrastructure
Cybersecurity analysts are currently focusing on the "Internet of Things" (IoT) as the primary vector for these attacks. As many businesses rush to digitize their operations, they are deploying "smart" systems—ranging from automated refrigeration units to bank transaction portals—that are connected to the public internet without sufficient security layers.
Laurens Singier, a lead researcher at the Cyber 3 Lab within the Howest University of Applied Sciences in Belgium, points to a systemic failure in the deployment of these devices. "Many organizations purchase industrial-grade equipment that comes pre-configured with default factory passwords," Singier noted. "When these devices are connected directly to the internet, they become low-hanging fruit for hackers. Furthermore, many of these devices operate on legacy software that contains known vulnerabilities, which are essentially open doors for anyone with the right tools."
The situation is further complicated by the democratization of cyber-weaponry. The rapid evolution of Generative Artificial Intelligence (AI) has allowed even low-skilled actors to generate sophisticated phishing campaigns, automate the discovery of vulnerable IP addresses, and write malicious code that can bypass standard firewalls. This has effectively lowered the barrier to entry for cyber-criminals, turning what was once a domain of state-sponsored actors into a playground for opportunistic syndicates.
Institutional Responses and Collective Defense
The European Union has moved to a high-alert status. Following the string of incidents, EU authorities held emergency meetings with national cybersecurity counterparts to discuss a collective, cross-border response strategy. The goal is to move away from isolated, nationalistic defense models toward a harmonized, "EU-wide" threat intelligence sharing network.
In the wake of the French blood bank and retail attacks, the European Union Agency for Cybersecurity (ENISA) has issued updated guidelines for critical infrastructure operators. The recommendations include:

- Mandatory MFA: Transitioning from simple password-based security to mandatory Multi-Factor Authentication (MFA) for all administrative interfaces.
- Network Segmentation: Ensuring that IoT devices (like HVAC systems) are strictly segmented from sensitive operational networks (like financial or medical databases).
- Hardware-Level Security: Moving away from standard internet-based connections to secure, private APNs (Access Point Names) or SIM-based cellular communication, which provides an additional layer of encryption.
- Continuous Monitoring: Implementing AI-driven monitoring that can detect anomalous traffic patterns—such as a refrigeration unit suddenly attempting to connect to an external server in a foreign jurisdiction.
Broader Implications for the Digital Economy
The implications of this wave of attacks extend far beyond immediate financial losses. They represent a fundamental challenge to the "Digitization First" strategy adopted by many European enterprises. If essential services, from food supply chains to medical logistics and banking, cannot be guaranteed to operate securely, the trust that underpins the modern digital economy risks erosion.
Furthermore, the attacks highlight the geopolitical dimension of cyber warfare. While the specific perpetrators of the Credit Mutuel Arkea attack remain under investigation, the nature of these strikes—targeting specific, localized infrastructure—often mirrors tactics used by groups seeking to destabilize civil order or demonstrate the fragility of Western institutions.
As investigators pore over logs and forensic data, the consensus among experts is that the "era of convenience" in digital infrastructure must come to an end. Organizations can no longer afford to prioritize connectivity over security. The future of European infrastructure will likely involve stringent, mandatory regulatory frameworks that require companies to prove the security of their "smart" devices before they are permitted to interface with the wider public internet.
For now, the focus remains on remediation and resilience. As the Paris prosecutor’s office continues its investigation and banks like Credit Mutuel Arkea bolster their perimeter security, the broader European business community is bracing for what may be a long and difficult transition toward a more hardened, security-conscious digital future. The message from the latest round of attacks is clear: in an interconnected world, the security of the whole is only as strong as the weakest connected device.
Related posts: