Global Cyber Emergency Unfolds as Critical PHP Vulnerabilities Spark 48-Hour Race Against Time

The global digital infrastructure faced an unprecedented stress test this week following the disclosure of two severe security flaws in PHP, one of the world’s most widely utilized programming languages. Dubbed "PHP2Shell" and cataloged under identifiers CVE-2026-109618 and CVE-2026-109619, the vulnerabilities triggered an intensive 48-hour global response from cybersecurity professionals, system administrators, and major technology firms racing to patch servers before widespread exploitation could take root.
The crisis underscored the systemic risks inherent in modern web infrastructure, where a single foundational software flaw can immediately jeopardize millions of enterprise systems, financial institutions, and government portals worldwide.
Anatomy of the PHP2Shell Vulnerabilities
The emergency began on October 21, when the core PHP development team rolled out emergency patches designed to neutralize two critical remote code execution (RCE) flaws. These vulnerabilities allowed unauthenticated malicious actors to execute arbitrary code on targeted servers remotely. Because no alternative configuration could fully substitute for installing the official software patches, developers were urged to update their systems immediately.
The scale of the threat quickly became apparent through automated scanning activity. Matthew Prince, CEO of cloud security and infrastructure giant Cloudflare, reported a dramatic surge in exploitation attempts on social media platform X. According to Cloudflare’s telemetry, thousands of probing attempts were recorded in the 10 hours leading up to the public disclosure. Within 45 minutes of the announcement, that number escalated to tens of thousands, reaching hundreds of thousands within two hours, and ultimately scaling to millions of probing attempts shortly thereafter.
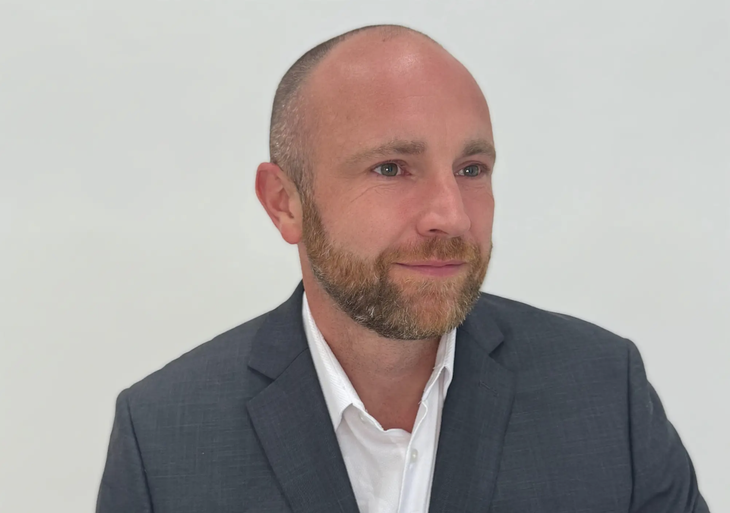
Nick Woodhead, founder of the artificial intelligence company GPTree and chief technology officer at Rothco and Compubox, described the intense operational pressure faced by technical teams during the initial disclosure window. "These types of security incidents are truly nightmares," Woodhead stated in an interview with Business Insider. Working through a grueling 48-hour shift with minimal sleep, Woodhead and his engineering peers discovered that remediation extended far beyond simply applying software patches. Teams had to actively audit systems to determine whether malicious actors had already penetrated environments or exfiltrated sensitive data prior to patching.
International Response and Financial Sector Impact
Given that PHP powers approximately 70% of all websites globally, the scope of potential disruption necessitated swift intervention by both private enterprises and government bodies. Major international organizations and financial institutions immediately elevated their threat alert levels.
In Japan, the Mitsubishi UFJ Financial Group temporarily suspended certain online banking services as a precautionary measure. Concurrently, Japan’s Ministry of Finance shut down specific content and services on its official websites to execute emergency security hardening procedures and verify system integrity. Similar defensive postures were adopted by government agencies and enterprise networks across Europe and North America.
Despite the massive volume of automated probing, major cybersecurity firms reported that widespread, successful exploitation campaigns had not yet materialized in the immediate aftermath of the disclosure. Amazon Threat Intelligence noted that its "honeypot" infrastructure, MadPot, had recorded scanning activity targeting PHP2Shell as early as October 17—several days before the vulnerabilities were officially made public. However, Amazon emphasized that it had not confirmed whether these early probes resulted in actual system compromises.
Similarly, a security advisory issued by CrowdStrike on October 23 confirmed that the firm had not observed widespread successful exploitation of the vulnerabilities across international enterprise environments or its own honeypot networks. CrowdStrike analysts pointed out that many of the initial proof-of-concept exploit scripts published online merely demonstrated the existence of the vulnerability rather than providing stable, reliable remote execution capabilities. To successfully compromise a target, attackers were required to customize and adapt their exploit code to match specific PHP versions and server configurations.
Remediation and Recommended Best Practices
The PHP development team released urgent security updates covering multiple active software branches, specifically targeting versions 8.2.35, 8.3.36, 8.4.27, and 8.5.12. Organizations utilizing older, end-of-life versions of PHP were instructed to urgently migrate to actively supported releases or implement robust web application firewall (WAF) rules as an interim mitigating defense.
Cybersecurity agencies in the United Kingdom, the United States, and other allied nations issued formal advisories urging all organizations to inventory their software dependencies, apply the official patches, and conduct thorough log analyses for indicators of compromise (IoCs). Where immediate patching was not technically feasible, authorities recommended evaluating localized risk and temporarily isolating vulnerable servers from external network connections.
Industry experts have stressed that the absence of widespread confirmed breaches does not equate to overall system safety. The velocity of exploitation attempts indicates that sophisticated threat actors are actively refining their tools. Security leaders have cautioned that organizations failing to audit their environments risk delayed-fuse compromises that could manifest weeks or months later.
A Turbulent Month for Enterprise Technology
For engineering leaders like Nick Woodhead, the PHP emergency was emblematic of an exceptionally volatile period for enterprise technology infrastructure. The crisis compounded existing operational pressures, arriving alongside emerging vulnerabilities in other foundational environments, such as Node.js—a runtime environment widely used for building scalable backend servers and web applications.
Reflecting on the relentless pace of vulnerability management, Woodhead remarked, "October certainly feels like an upside-down month for the technology sector."
As the immediate 48-hour emergency phase subsides into long-term remediation and monitoring, the incident serves as a stark reminder of the fragile interdependencies underpinning the global digital economy. Continuous vulnerability scanning, rapid patch management, and zero-trust architectural principles remain critical defenses as organizations navigate an increasingly complex and hostile cybersecurity landscape.