South Korea Deploys Emergency Security Overhaul After Major Passport Data Leak Compromises President Lee Jae Myung and Senior Officials

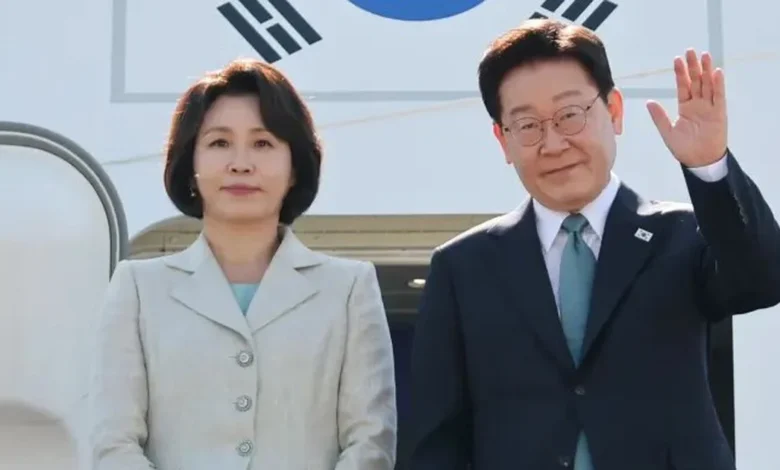
The South Korean government has announced the immediate deployment of comprehensive emergency countermeasures following a massive and unprecedented security breach that exposed the sensitive passport details of 168 high-ranking individuals, including President Lee Jae Myung, First Lady Kim Hea Kyung, and numerous top-tier government officials. The breach, which went undetected for nearly five months, has triggered deep alarm within the national security apparatus and raised serious questions regarding the digital resilience of government data management systems.
The compromised information, which includes passport numbers, dates of birth, issue dates, and expiration dates, was made publicly accessible on an obscure, subscription-based code-checking website. As South Korea grapples with the fallout of this major cybersecurity failure, administration officials are scrambling to contain the diplomatic, personal, and operational risks associated with having the sovereign’s highest-ranking leadership exposed to potential identity theft, international surveillance, or malicious targeting.
Anatomy of a Five-Month Security Breach
According to investigative reports published by major South Korean media outlets, including the Chosun Ilbo and the Korean Broadcasting System (KBS), the leak originated from an Excel spreadsheet titled "Passenger List for Presidential Special Flight (South Korea – Britain)." The file contained the complete travel roster and identification credentials of individuals who accompanied President Lee Jae Myung on his state visit to the United Kingdom and his subsequent participation in the G7 summit and European tour in June.
Digital forensics indicate that the sensitive data was uploaded to an unauthorized third-party verification platform as early as June, roughly one week before the presidential delegation’s departure. For nearly five months, the file remained accessible to anyone utilizing the platform’s code-checking services, completely bypassing the notice of internal cybersecurity monitors. It was only recently that investigative journalists uncovered the exposed directory and alerted authorities, prompting an immediate scramble across government agencies.
The breach is not merely an administrative oversight; it represents a profound breach of state security protocols. Passports of heads of state and senior cabinet members are protected under rigorous confidentiality standards precisely because their exposure can facilitate targeted espionage, unauthorized travel tracking, and fraudulent activities on the global stage.
A Who’s Who of South Korea’s Leadership Exposed
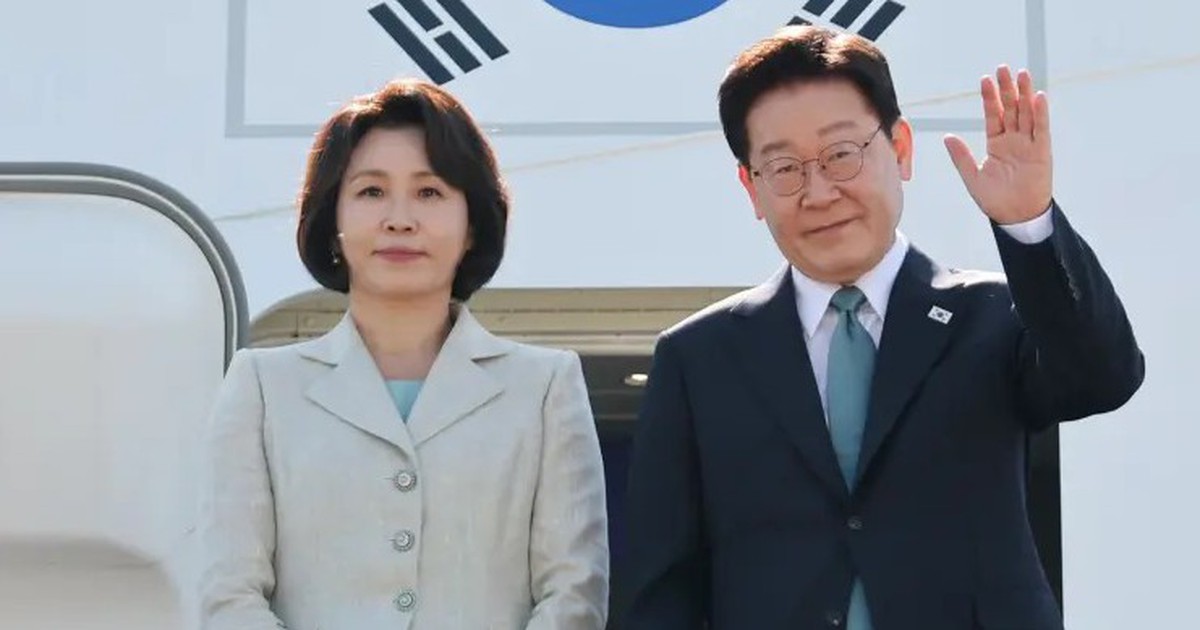
The scale of the leak is vast, compromising the personal documentation of 168 people. Beyond President Lee Jae Myung and First Lady Kim Hea Kyung, the exposed roster reads like a directory of the nation’s core executive branch and national security leadership.
Among those whose passport details were leaked are Chief Presidential Secretary for Policy Kim Yong Beom, National Security Advisor Wi Sung Lac, Deputy Prime Minister and Minister of Science and Information Technology Bae Kyung Hoon, Foreign Minister Cho Hyun, and Minister of SMEs and Startups Han Seong Sook.
Furthermore, the compromised database extended well beyond political appointees. It included the personal and professional credentials of working-level personnel from the Office of the President, the Ministry of Foreign Affairs, the Presidential Security Service, and accredited journalists who were granted clearance to travel alongside the presidential entourage. The inclusion of security personnel and diplomatic aides is considered particularly dangerous, as it potentially maps out the logistical and protective framework surrounding South Korea’s executive leadership during international engagements.
Immediate Government Response and Crisis Management
In response to the revelations, the Presidential Office issued a formal statement acknowledging the breach and confirming that swift containment measures had been enacted. "The administration has taken this security lapse with the utmost gravity and has immediately deployed emergency response protocols to mitigate any potential risks," a senior presidential spokesperson stated.
The Office of the President is currently coordinating a joint task force with the Ministry of Foreign Affairs, the National Intelligence Service (NIS), and cyber-investigative units from the national police. The primary objective of this task force is to determine how the classified manifest was transferred from secure government servers to an external, commercial website, and to identify any malicious actors who may have downloaded or exploited the data during the five months it remained online.
Diplomatic channels have also been activated. The Ministry of Foreign Affairs is reportedly in contact with international partners and aviation authorities to ensure that the compromised passport numbers are flagged, preventing potential fraudulent use or unauthorized attempts to book international travel under the identities of South Korea’s highest officials. Moreover, steps are being taken to reissue new diplomatic passports with updated identifiers for all affected individuals.
Broader Implications for National Cybersecurity
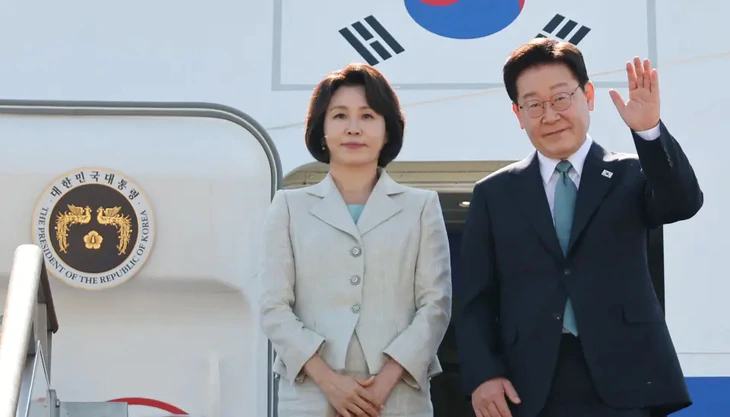
The incident has ignited a fierce political and public debate regarding South Korea’s institutional cybersecurity posture. Despite boasting one of the world’s most advanced digital infrastructures and high-speed internet networks, South Korea has repeatedly faced high-profile data leaks involving public sector databases.
Cybersecurity experts point out that the reliance on third-party vendors, administrative laxity, and inadequate auditing of document-sharing practices remain persistent vulnerabilities within government agencies. When handling sensitive travel manifests for presidential delegations, protocols typically dictate strict, encrypted, and isolated data handling procedures. The fact that a classified passenger list ended up on an open-access code-verification platform suggests a catastrophic failure of basic digital hygiene.
Opposition lawmakers have seized upon the incident to demand accountability, calling for an urgent parliamentary audit into the Presidential Security Service and the Ministry of Foreign Affairs. Critics argue that if the government cannot secure the personal data of its own president and national security advisors, the administration’s broader cybersecurity initiatives aimed at protecting critical national infrastructure and private citizens’ data ring hollow.
Potential Fallout and Next Steps
As the investigation unfolds, the immediate priority remains damage control. Authorities must ascertain whether the leaked data was accessed by hostile foreign intelligence entities or cybercriminal syndicates. While identity theft and financial fraud are immediate concerns, the strategic implications—such as the mapping of high-level diplomatic movements and security details—pose a far graver threat.
The Presidential Office has pledged a transparent accounting of the investigation’s findings once initial containment and remediation steps are complete. In the interim, the administration faces mounting pressure to overhaul its internal data governance framework, implement stricter access controls, and enforce severe penalties for administrative negligence. For President Lee Jae Myung’s administration, this security breach serves as a stark and embarrassing reminder that in an increasingly interconnected digital age, the most formidable threats to national security often begin with a single, misplaced file.
Related posts: